There is no single AI compliance deadline. There is a calendar of them, each attached to a particular jurisdiction, a particular kind of organisation, and a particular thing that organisation does.
A company running a customer chatbot in Germany crossed a real line on 2 August 2026. A company training frontier models in California crossed one on 1 January 2026. A company doing neither may have no AI-specific deadline at all this year, and the honest answer for them is: none of this binds you yet.
This page keeps the dates in one place.
Last reviewed: 17 September 2026.
This page is maintained as a living reference. It is reviewed monthly and updated when a significant regulatory event occurs — an amendment, a court decision, a delayed applicability date, or new implementing guidance. Every row in the master table carries its own Last verified date.
Regulatory dates change, and several in this table already have. Verify the linked primary source before making a compliance decision.
This tracker is provided for informational purposes and is not legal advice. Regulatory requirements can depend on an organization’s jurisdiction, role, system, sector, and specific facts. Always verify the current primary-source text and applicable guidance before making compliance decisions.
Key Takeaways
- The EU AI Act’s biggest deadline moved, and most people have the wrong date. Regulation (EU) 2026/1744 — the Digital Omnibus on AI — entered into force on 27 July 2026 and pushed standalone high-risk obligations from 2 August 2026 to 2 December 2027, and embedded high-risk systems to 2 August 2028.
- 2 August 2026 still landed. Article 50 transparency duties, general application of the Act, and the AI Office’s enforcement powers over GPAI model providers all took effect as originally scheduled. Only Chapter III moved.
- Two new EU prohibitions arrive on 2 December 2026, covering AI systems that generate non-consensual intimate material or child sexual abuse material. They sit in the Article 5 tier, with fines up to €35 million or 7% of worldwide turnover.
- Colorado’s AI Act never took effect. SB 24-205 was repealed by SB 26-189, signed 14 May 2026. A narrower automated decision-making regime applies from 1 January 2027.
- The United States has no federal AI statute. Executive Order 14365 directs agencies to challenge state AI laws, but no federal law or court has preempted any of them. State requirements remain enforceable.
- 1 January 2027 is the densest date on the calendar: Colorado’s ADMT Act, New York’s RAISE Act, Illinois SB 315 and California’s CPPA ADMT compliance date all land together.
- Most obligations bind providers and developers, not deployers — but Article 50, Connecticut’s employment provisions and Colorado’s notice duties all reach the organisation using the system.
Quick Navigation
- The AI Compliance Deadline Calendar
- EU AI Act Compliance Deadlines
- GPAI Compliance Deadlines
- U.S. AI Compliance Deadlines
- Colorado's AI Compliance Deadline
- State AI Compliance Deadlines
- International AI Compliance Deadlines
- How to Read an AI Compliance Deadline
- What to Do Before an AI Compliance Deadline
- Why AI Compliance Deadlines Keep Moving
- How We Maintain This Tracker
- Sources
- Frequently Asked Questions
The AI Compliance Deadline Calendar
This is the reference table. It covers enacted, operative instruments with firm dates. Rows are chronological. “Status” describes the legal position as of the last review date, not a judgement about severity.
| Date | Jurisdiction | Regulation / Rule | What changes | Who it applies to | What is actually required | Status | Last verified |
|---|---|---|---|---|---|---|---|
| 1 Aug 2024 | EU | AI Act, Reg. (EU) 2024/1689 | Entry into force — no obligations attach | — | Nothing yet; starts the Art. 113 clock | In force | 17 Sep 2026 |
| 2 Feb 2025 | EU | AI Act Arts. 4, 5 | Prohibited practices; AI literacy | Providers, deployers | Cease prohibited uses; take measures supporting AI literacy | Applicable | 17 Sep 2026 |
| 2 Aug 2025 | EU | AI Act Ch. V, VII, XII | GPAI obligations; governance; penalties | GPAI model providers | Technical documentation, downstream information, copyright policy, training-content summary; systemic-risk models add evaluation, adversarial testing, incident reporting, cybersecurity | Applicable | 17 Sep 2026 |
| 1 Sep 2025 | China | AI content labelling measures | Labelling of AI-generated content | Service providers in China | Explicit and implicit labelling of synthetic content | In force | 17 Sep 2026 |
| 1 Jan 2026 | US — California | SB 53 (TFAIA) | Frontier model transparency | Frontier / large frontier developers | Publish frontier AI framework and transparency reports; report critical safety incidents; whistleblower protections | In force | 17 Sep 2026 |
| 1 Jan 2026 | US — California | AB 2013 | Training-data transparency | Developers of generative AI systems offered to Californians | Publish high-level training-data documentation | In force | 17 Sep 2026 |
| 1 Jan 2026 | US — California | CPPA regulations | ADMT, risk assessment and cybersecurity audit rules effective | CCPA-covered businesses | Prospective risk-assessment duties begin; ADMT duties phased (see 2027) | In force | 17 Sep 2026 |
| 1 Jan 2026 | US — Texas | TRAIGA (HB 149) | Comprehensive AI governance regime | Developers and deployers in Texas | Prohibited-use restrictions; disclosure duties; AG enforcement with civil penalties | In force | 17 Sep 2026 |
| 1 Jan 2026 | US — Illinois | HB 3773 | AI in employment decisions | Employers | Non-discrimination and notice duties under the Human Rights Act | In force | 17 Sep 2026 |
| 22 Jan 2026 | South Korea | AI Basic / Framework Act + Enforcement Decree | Comprehensive national AI framework | Operators serving Korean users, incl. foreign | Advance user notice for generative and high-impact AI; labelling; risk management for high-impact AI; domestic representative where triggered | In force (transitional enforcement grace) | 17 Sep 2026 |
| 19 May 2026 | US — Federal | TAKE IT DOWN Act, §3 | Notice-and-removal duties enforceable | Covered platforms hosting user-generated content | Clear removal process; remove valid NCII reports and known identical copies within 48 hours | In force; FTC enforcing | 17 Sep 2026 |
| 27 Jul 2026 | EU | Digital Omnibus on AI, Reg. (EU) 2026/1744 | Amends the AI Act; defers high-risk dates | — | Amendments become part of the AI Act | In force | 17 Sep 2026 |
| 2 Aug 2026 | EU | AI Act Art. 50; general application | Transparency duties; AI Office enforcement powers live | Providers and deployers of interactive / synthetic-content systems; GPAI model providers | Disclose AI interaction; mark synthetic output machine-readably; label deepfakes; GPAI enforcement now active | Applicable | 17 Sep 2026 |
| 2 Aug 2026 | US — California | SB 942 as amended by AB 853 | Covered provider obligations operative | Generative AI providers >1M monthly users | Free AI detection tool; optional manifest disclosure; latent disclosure in image, video, audio; flow-down to licensees | In force | 17 Sep 2026 |
| 1 Oct 2026 | US — Connecticut | SB 5 (CART Act), P.A. 26-15 | First tranche of AI duties | Employers; AEDT developers; large synthetic-media providers; frontier developers | AEDT anti-discrimination and developer-to-deployer documentation; provenance for 1M+ user providers; subscription disclosures; WARN notice AI disclosure; whistleblower protections | Upcoming | 17 Sep 2026 |
| 2 Dec 2026 | EU | AI Act Art. 5(1)(ba),(bb) via Reg. 2026/1744 | Two new prohibitions | Providers and deployers | No placing on market, putting into service, or use of AI generating or manipulating non-consensual intimate material or CSAM | Upcoming | 17 Sep 2026 |
| 2 Dec 2026 | EU | AI Act Art. 50(2) / Art. 111(4) | Legacy marking grace period ends | Providers of generative systems on the market before 2 Aug 2026 | Machine-readable marking of synthetic output | Upcoming | 17 Sep 2026 |
| 1 Jan 2027 | US — Colorado | SB 26-189 (ADMT Act) | Replaces repealed SB 24-205 | Developers and deployers of covered ADMT | Developer technical documentation and update notices; deployer point-of-interaction notice; 30-day adverse-outcome explanation; access, correction and human-review rights; 3-year records | Upcoming | 17 Sep 2026 |
| 1 Jan 2027 | US — New York | RAISE Act (as amended 27 Mar 2026) | Frontier model safety regime | Large frontier developers | Safety protocol publication; incident reporting; AG enforcement | Upcoming | 17 Sep 2026 |
| 1 Jan 2027 | US — Illinois | SB 315 (AI Safety Measures Act) | Frontier AI safety regime takes effect | Frontier developers (revenue-tiered) | Disclosure and whistleblower duties from this date; framework and audit duties from 1 Jan 2028 | Upcoming | 17 Sep 2026 |
| 1 Jan 2027 | US — California | CPPA ADMT provisions | ADMT compliance date | CCPA-covered businesses using ADMT for significant decisions | Pre-use notice, opt-out, access to decision logic; pre-2027 systems must be brought into compliance | Upcoming | 17 Sep 2026 |
| 1 Jan 2027 | US — California | SB 942 / AB 853 tranche 2 | Platform duties begin | Generative AI hosting platforms; large online platforms | Ensure downloadable systems carry disclosures; detect and surface provenance data | Upcoming | 17 Sep 2026 |
| 2 Aug 2027 | EU | AI Act Art. 111 | Legacy GPAI compliance date | Providers of GPAI models on the market before 2 Aug 2025 | Bring pre-existing models into Chapter V compliance | Upcoming | 17 Sep 2026 |
| 2 Aug 2027 | EU | AI Act Art. 57 via Reg. 2026/1744 | Sandbox obligation deferred to this date | Member States | At least one national AI regulatory sandbox operational | Upcoming | 17 Sep 2026 |
| 1 Oct 2027 | US — Connecticut | SB 5 (CART Act) | AEDT deployer duties operative | Employers using AEDT | Pre-decision notice and disclosure to applicants and employees | Upcoming | 17 Sep 2026 |
| 2 Dec 2027 | EU | AI Act Ch. III, Annex III | Standalone high-risk obligations apply | Providers, deployers, importers, distributors of Annex III systems | Conformity assessment, QMS, technical documentation, logging, human oversight, CE marking, EU database registration, FRIA where applicable | Upcoming (deferred from 2 Aug 2026) | 17 Sep 2026 |
| 1 Jan 2028 | US — Illinois | SB 315 | Framework and audit duties begin | Large frontier developers | Published catastrophic-risk framework; annual independent third-party audit | Upcoming | 17 Sep 2026 |
| 2 Aug 2028 | EU | AI Act Art. 6(1), Annex I | Embedded high-risk obligations apply | Product manufacturers and providers under Annex I legislation | High-risk requirements for AI in regulated products | Upcoming (deferred from 2 Aug 2027) | 17 Sep 2026 |
The rest of this page explains the rows that need explaining.
EU AI Act Compliance Deadlines
The single most common error in EU AI Act compliance planning is treating entry into force as a deadline. It is not.
Regulation (EU) 2024/1689 entered into force on 1 August 2024. That date started the clock. It imposed nothing. Individual obligations become applicable on the separate dates set out in Article 113, and those dates have since been amended.
2 February 2025 — Prohibitions and AI literacy
Chapters I and II applied. The Article 5 prohibited practices became enforceable, and the Article 4 AI literacy duty attached to providers and deployers. The Digital Omnibus later rewrote Article 4 from a duty to ensure AI literacy into a duty to take measures to support its development — an obligation of effort rather than of result.
2 August 2025 — GPAI obligations and governance
Chapter V applied to providers of general-purpose AI models, alongside the governance and penalty framework. Crucially, the Commission’s power to actually enforce those GPAI rules did not arrive with them.
2 August 2026 — General application, Article 50, and live GPAI enforcement
This is the date that mattered most in 2026, and the one most widely assumed to have been cancelled.
It was not. The Act reached its general date of application. Article 50 transparency obligations became directly applicable to providers and deployers: users must be told when they are interacting with an AI system, and synthetic audio, image, video and text must be marked in a machine-readable format. Deepfake and public-interest-text disclosure duties fall on deployers.
On the same date, the AI Office and national market surveillance authorities gained their supervision and enforcement powers, including over GPAI model providers. Article 50 breaches sit in the Article 99(4) band — up to €15 million or 3% of worldwide turnover, whichever is higher.
If you run a chatbot for EU users or publish synthetic media into the EU market, your deadline has passed.
2 December 2026 — New prohibitions and the marking grace period
Two things land together.
First, the new Article 5 prohibitions added by the Digital Omnibus apply: AI systems intended to generate or manipulate non-consensual intimate material or child sexual abuse material. The Council’s own framing named the “nudify app” category directly. These sit in the prohibited-practices tier, at up to €35 million or 7% of turnover.
Second, the transitional window closes for Article 50(2). Providers of generative systems placed on the market before 2 August 2026 were given a grace period to implement machine-readable marking. The Omnibus cut that window from six months to three, fixing the date at 2 December 2026. Systems launched after 2 August 2026 never had a grace period.
2 December 2027 and 2 August 2028 — High-risk obligations
Chapter III Sections 1–3 now apply from 2 December 2027 for standalone Annex III systems — recruitment, credit scoring, education, essential services, law enforcement, migration, administration of justice — and from 2 August 2028 for AI embedded in products already covered by Annex I harmonization legislation.
The obligations themselves did not change. Conformity assessment, quality management systems, technical documentation, logging, human oversight, CE marking, EU database registration and fundamental rights impact assessments all survive intact. Only the clock moved, and it moved because the harmonised standards and national authority designations were not ready.
Two smaller Omnibus dates are worth calendaring: at least one national AI regulatory sandbox must be operational by 2 August 2027, and the Commission must publish coordination guidance for Annex I sectors by 1 August 2027.
GPAI Compliance Deadlines
General-purpose AI obligations deserve separate treatment because they bind a narrow population and are routinely misapplied to a wide one.
The obligations fall on providers of GPAI models. Not on companies that build applications using those models. If you call an API, you are a downstream deployer or a provider of an AI system — you are not a GPAI model provider, and Articles 51–55 do not attach to you.
Two dates govern:
- 2 August 2025 — Chapter V applied to GPAI models placed on the EU market from that date. Providers must maintain technical documentation, supply information to downstream providers, put a copyright policy in place, and publish a sufficiently detailed summary of training content. Providers of models with systemic risk carry additional model evaluation, adversarial testing, incident reporting and cybersecurity duties.
- 2 August 2027 — the Article 111 transitional rule. Providers of GPAI models already on the market before 2 August 2025 have until this date to bring those models into compliance.
Between August 2025 and August 2026, Chapter V was effectively compliance on paper: the obligations existed, the Commission’s enforcement machinery did not. That gap closed on 2 August 2026. GPAI model providers now answer to the AI Office directly, on a deliberately centralised basis, with exposure up to €15 million or 3% of worldwide turnover.
U.S. AI Compliance Deadlines
The United States has no comprehensive federal AI Act. Anyone telling you otherwise is describing an executive order or a bill.
Compliance runs across three layers, and they do not align.
Federal executive action. Executive Order 14365, Ensuring a National Policy Framework for Artificial Intelligence, was signed on 11 December 2025 and published in the Federal Register on 16 December 2025. It directs the Attorney General to establish an AI Litigation Task Force to challenge state AI laws, conditions certain discretionary and broadband funding on state regulatory restraint, and asks for a legislative recommendation for a preemptive federal framework.
An executive order cannot preempt state law. Only Congress or a court can. As of this review, no federal statute and no court decision has preempted or stayed any state AI law, and a bipartisan coalition of state attorneys general has publicly opposed broad preemption. State AI requirements remain enforceable and should be treated as live.
Federal statute. One genuinely federal deadline has already passed. The TAKE IT DOWN Act’s notice-and-removal requirements became enforceable on 19 May 2026. Covered platforms hosting user-generated content must provide a clear removal process for non-consensual intimate imagery — including AI-generated forgeries — and remove valid reports, plus known identical copies, within 48 hours. The FTC began enforcement on that date, with civil penalties assessed per violation.
Sector regulators. Existing law already applies to AI without naming it. The FTC issued a Section 5 policy statement on AI in March 2026; financial, health and employment regulators continue to apply existing authorities. There is no new deadline here, which is precisely why it gets missed.
Colorado’s AI Compliance Deadline
Colorado is the clearest illustration of why a tracker needs date-stamped rows.
SB 24-205, the Colorado Artificial Intelligence Act, was signed in May 2024 with an effective date of 1 February 2026. A special-session bill, SB 25B-004, pushed that to 30 June 2026. In April 2026 a federal magistrate stayed enforcement. The law never took effect at any point.
On 14 May 2026, Governor Polis signed SB 26-189, the Automated Decision-Making Technology Act (Chapter 131 of the 2026 Session Laws). It repeals and reenacts the SB 24-205 framework as something materially narrower. The reasonable-care duty, the algorithmic-discrimination impact assessments and the risk-management-programme mandate are gone — and with them the affirmative defence for aligning to the NIST AI RMF.
Effective 1 January 2027, for decisions made on or after that date.
Who it binds. Developers and deployers of automated decision-making technology used to materially influence a consequential decision — one relating to access to, eligibility for, or compensation related to education, employment, housing, financial or lending services, insurance, health-care services, or essential government services and public benefits.
What developers must do. Provide deployers with technical documentation covering intended uses, categories of training data, known limitations, and instructions for appropriate use and human review. Notify deployers of material updates. Retain compliance records for at least three years.
What deployers must do. Give consumers clear and conspicuous notice at the point of interaction. Where a covered ADMT produces an adverse outcome, provide a plain-language description of its role within 30 days. Honour consumer rights to access and correct personal data, and to request meaningful human review and reconsideration.
Enforcement. The Attorney General, through the Colorado Consumer Protection Act; a violation is a deceptive trade practice. Before 1 January 2030, the AG must give 60 days’ notice and an opportunity to cure where a cure is possible. There is no private right of action, though the Act allocates fault between developers and deployers in existing discrimination claims.
One item to watch: the AG must adopt rules clarifying the post-adverse-outcome disclosure requirements by 1 January 2027. Those rules will determine much of the operational detail.
State AI Compliance Deadlines
Enacted regimes with operative dates only.
| State | Instrument | Effective | Binds | Core duty |
|---|---|---|---|---|
| California | SB 53 (TFAIA) | 1 Jan 2026 | Frontier developers | Safety framework, transparency reports, incident reporting |
| California | AB 2013 | 1 Jan 2026 | Generative AI developers | Training-data documentation |
| California | SB 942 / AB 853 | 2 Aug 2026 → 2028 | Providers, platforms, device makers | Detection tool, manifest and latent disclosures, provenance |
| California | CPPA regulations | 1 Jan 2026 → 1 Jan 2027 | CCPA-covered businesses | Risk assessments; ADMT notice, opt-out, logic access |
| Texas | TRAIGA (HB 149) | 1 Jan 2026 | Developers and deployers | Prohibited uses, disclosure, AG enforcement |
| Illinois | HB 3773 | 1 Jan 2026 | Employers | Employment AI non-discrimination and notice |
| Illinois | SB 315 | 1 Jan 2027 / 1 Jan 2028 | Frontier developers | Disclosure, whistleblower; then framework and audit |
| Connecticut | SB 5 (CART Act) | 1 Oct 2026 → 1 Jan 2028 | Employers, providers, platforms | AEDT duties, provenance, companion-chatbot rules |
| New York | RAISE Act | 1 Jan 2027 | Large frontier developers | Safety protocols, incident reporting |
| Colorado | SB 26-189 (ADMT Act) | 1 Jan 2027 | Developers and deployers | Documentation, notice, explanation, human review |
Three patterns are worth naming.
- A frontier-model template has emerged. California SB 53, New York’s RAISE Act and Illinois SB 315 share definitions, compute thresholds and structure. All three reach developers training models above roughly 10²⁶ operations; the heavier duties attach to those also clearing $500 million in revenue. If you are not training frontier models, none of them bind you. Illinois went furthest, adding the first mandatory annual third-party audit requirement in U.S. law — from 1 January 2028, not 2027.
- Transparency laws bind providers; employment laws bind employers. California’s AI Transparency Act (SB 942, as amended by AB 853) phases in by role: covered providers from 2 August 2026, generative AI hosting platforms and large online platforms from 1 January 2027, capture device manufacturers from 1 January 2028. Connecticut’s SB 5 reaches employers directly.
- Privacy regulation is doing AI regulation’s work. California’s CPPA regulations took effect on 1 January 2026, but the ADMT-specific duties — pre-use notice, opt-out, access to decision logic — bind from 1 January 2027, with risk assessments for pre-2026 processing due by 31 December 2027 and first summary reporting on 1 April 2028. For most businesses this is a larger operational lift than any AI-specific statute.
International AI Compliance Deadlines
Only jurisdictions with a firm, operative milestone appear here.
South Korea is the substantive one. The Framework Act on the Development of Artificial Intelligence (the AI Basic Act) and its Enforcement Decree took effect on 22 January 2026. It applies extraterritorially to foreign businesses whose AI activities affect Korean users, sets a high-impact threshold at 10²⁶ FLOPs, requires advance notice to users of generative and high-impact AI, mandates labelling of outputs hard to distinguish from human-made content, and can require foreign operators to designate a domestic representative. Fines are modest by EU standards, and a transitional grace period on enforcement applies for roughly the first year.
China enforces a stack of binding measures rather than a single act. The AI content labelling measures have applied since 1 September 2025, alongside existing generative AI and algorithm filing requirements.
The United Kingdom, Canada, Australia, Japan, Singapore and Brazil do not currently have a horizontal AI statute with a firm compliance deadline. The UK remains regulator-led with no general AI Act. Canada’s AIDA died on the order paper and has not been revived. Singapore’s agentic AI governance framework is voluntary. Brazil’s PL 2338 has not completed passage. Saying so plainly is more useful than inventing a date.
How to Read an AI Compliance Deadline
A date alone tells you almost nothing. Six things in sequence tell you everything.
Date → Jurisdiction → Role → System → Obligation → Evidence.
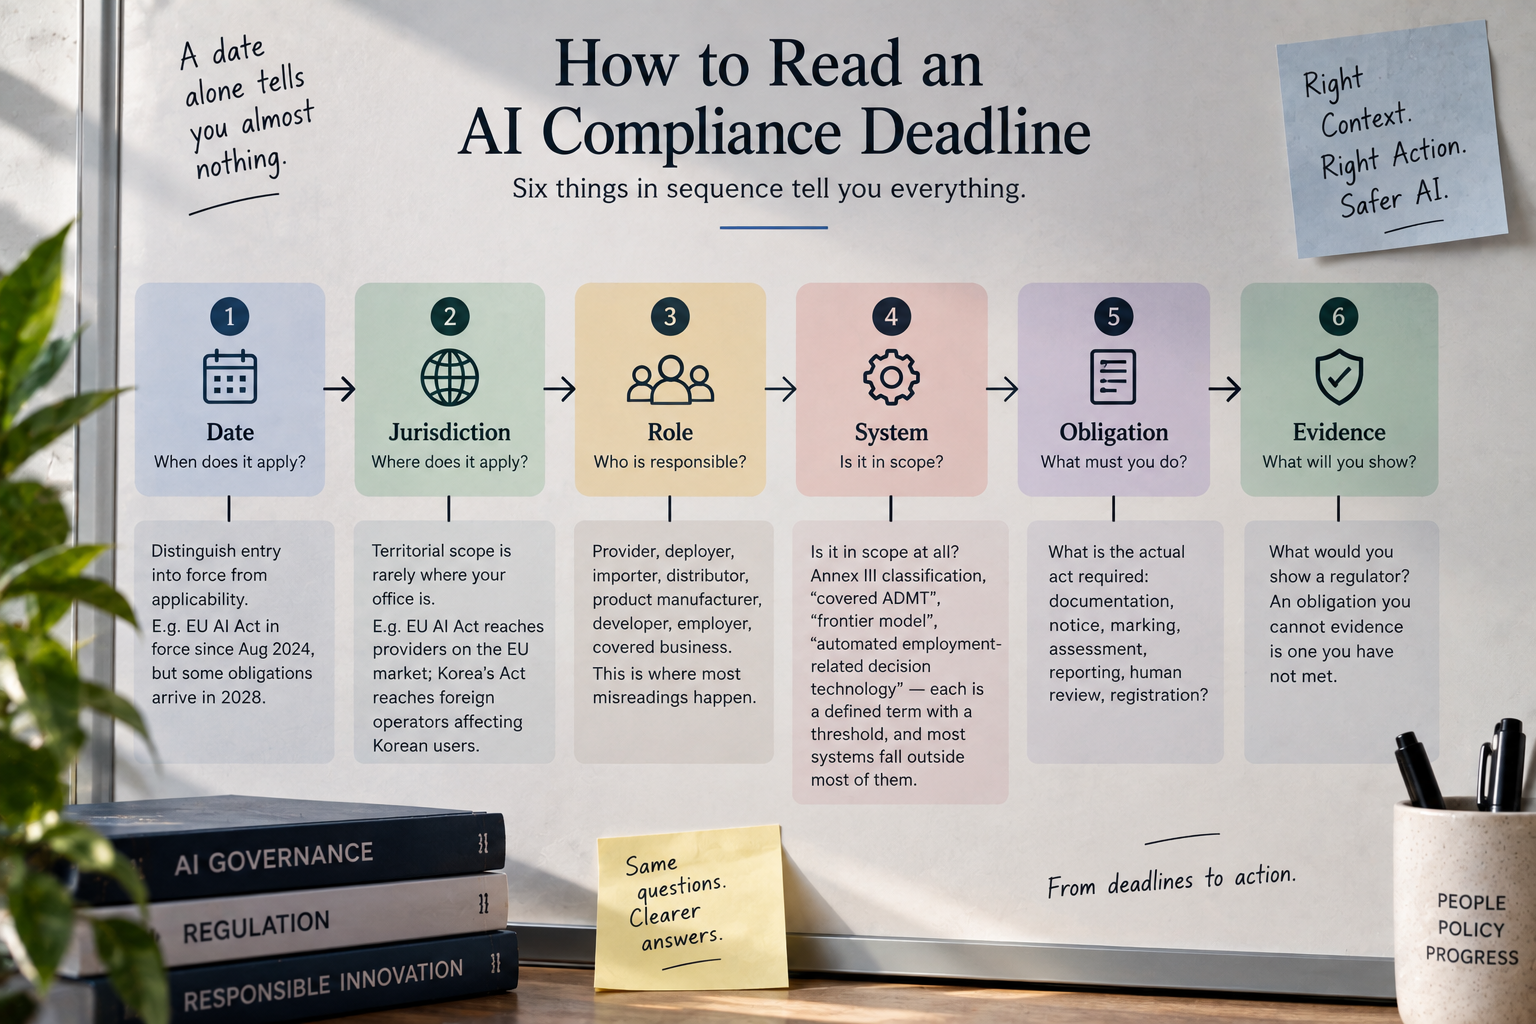
- Date. Distinguish entry into force from applicability. The EU AI Act has been in force since August 2024 and still has obligations arriving in 2028.
- Jurisdiction. Territorial scope is rarely where your office is. The EU AI Act reaches providers placing systems on the EU market; Korea’s Act reaches foreign operators affecting Korean users.
- Role. Provider, deployer, importer, distributor, product manufacturer, developer, employer, covered business. This is where most misreadings happen. GPAI obligations bind model providers. Article 50 deepfake duties bind deployers. Colorado splits duties between developers and deployers with different content.
- System. Is it in scope at all? Annex III classification, “covered ADMT”, “frontier model”, “automated employment-related decision technology” — each is a defined term with a threshold, and most systems fall outside most of them.
- Obligation. What is the actual act required: documentation, notice, marking, assessment, reporting, human review, registration?
- Evidence. What would you show a regulator? An obligation you cannot evidence is one you have not met.
Run any row of the table through those six and you will know whether it is yours.
What to Do Before an AI Compliance Deadline
- Re-check the primary source in the month before the date. Two of the dates on this page moved in the last year.
- List the jurisdictions where your systems are placed on the market, put into service, or reach users. Not where you are incorporated.
- Inventory your AI systems. Include vendor tools and embedded features. The systems that cause problems are the ones nobody registered as AI.
- Assign a role per system per jurisdiction. The same organisation is often a provider in one relationship and a deployer in another.
- Classify. Does the system meet the definitional threshold — Annex III, covered ADMT, frontier model, AEDT?
- Map obligations to the classification, not to the headline. Most deadlines carry a handful of duties, not all of them.
- Name an accountable owner per obligation. A calendar entry with no owner is a missed deadline with a paper trail.
- Build the documentation now. Technical documentation, training-data summaries and instructions for use take longer than the notice text does.
- Instrument logging and incident detection. Incident reporting duties assume you can detect the incident.
- Review your model and vendor dependencies. Your obligations often depend on what your upstream provider gives you.
Why AI Compliance Deadlines Keep Moving
Not political weather. Structural mechanics, and each produces a different kind of change.
- Amendments. The Digital Omnibus is the clearest case: a regulation amending a regulation, moving dates without reopening substance.
- Missing implementation infrastructure. The EU high-risk deferral happened largely because harmonised standards from CEN-CENELEC and national competent authority designations were not ready. An obligation whose compliance tools do not exist is not enforceable in practice.
- Legislative replacement. Colorado did not delay its law a third time. It repealed and rewrote it, which changes the obligations, not just the date.
- Litigation. A federal magistrate stayed SB 24-205 before it took effect. Court decisions can pause a date without touching the text.
- Agency rulemaking. Colorado’s AG rules and the CPPA’s phased schedule determine what a statutory date actually requires.
- Federal-state conflict. EO 14365’s machinery is running. It has changed no obligation yet, but it is the most likely source of movement in the U.S. rows.
How We Maintain This Tracker
Stated plainly, because a maintenance claim is only useful if it is accurate.
- Primary sources first. Dates come from the Official Journal, EUR-Lex, the Federal Register, state legislature records and regulator publications. Law firm and consultancy analysis is used to interpret provisions, never to establish a date.
- Per-row date stamps. Every row carries its own Last verified date, because rows are not all checked with equal frequency.
- Monthly review of the full table, plus an event-driven update when a significant development occurs.
- Discrepancies are disclosed, not resolved silently. Where reputable sources disagree, the page says so and identifies which source is closer to the primary text.
- Change notes are recorded in the Update History at the foot of the page.
- No predictive dates. Where a date is not fixed, the table says “Not yet fixed” rather than estimating.
The calendar moves. The page moves with it, or it is worth nothing.
Sources
Tier 1 — primary legal and regulatory sources
- Regulation (EU) 2024/1689 (AI Act), EUR-Lex —
https://eur-lex.europa.eu/eli/reg/2024/1689/oj - Regulation (EU) 2026/1744 (Digital Omnibus on AI), EUR-Lex —
https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX%3A32026R1744 - Council of the EU press release, final adoption, 29 June 2026 —
https://www.consilium.europa.eu/en/press/press-releases/2026/06/29/artificial-intelligence-council-gives-final-green-light-to-simplify-and-streamline-rules/ - Council of the EU press release, political agreement, 7 May 2026 —
https://www.consilium.europa.eu/en/press/press-releases/2026/05/07/artificial-intelligence-council-and-parliament-agree-to-simplify-and-streamline-rules/ - Executive Order 14365, Ensuring a National Policy Framework for Artificial Intelligence —
https://www.whitehouse.gov/wp-content/uploads/2025/12/eo-14365.pdf - Colorado SB 26-189, Colorado General Assembly —
https://leg.colorado.gov/bills/sb26-189 - FTC, “FTC Begins Enforcing the TAKE IT DOWN Act” —
https://www.ftc.gov/news-events/news/press-releases/2026/05/ftc-begins-enforcing-take-it-down-act - FTC, warning letters to platforms —
https://www.ftc.gov/news-events/news/press-releases/2026/05/ftc-sends-warning-letters-companies-about-compliance-take-it-down-act - EU law procedure tracker for the Digital Omnibus —
https://law-tracker.europa.eu/procedure/2025_359?lang=en
Tier 2 — standards and official guidance
- NIST AI Risk Management Framework —
https://www.nist.gov/itl/ai-risk-management-framework - International Trade Administration briefing, South Korea AI Basic Act —
https://www.trade.gov/market-intelligence/south-korea-ai-basic-act
Frequently Asked Questions
When does the EU AI Act apply?
In phases, not all at once. Regulation (EU) 2024/1689 entered into force on 1 August 2024. Prohibited practices and AI literacy duties applied from 2 February 2025, GPAI obligations from 2 August 2025, and the Act reached general application — including Article 50 transparency duties — on 2 August 2026. High-risk obligations now apply from 2 December 2027 for standalone Annex III systems and 2 August 2028 for AI embedded in regulated products.
Were the EU AI Act’s high-risk deadlines cancelled?
No. They were deferred. Regulation (EU) 2026/1744, the Digital Omnibus on AI, entered into force on 27 July 2026 and moved the dates. The substantive obligations — conformity assessment, quality management systems, technical documentation, logging, human oversight, CE marking, database registration — are unchanged. Only the clock moved.
When do GPAI obligations apply, and who do they bind?
They bind providers of general-purpose AI models, not companies that build applications on top of those models. Obligations applied from 2 August 2025 for models placed on the EU market from that date. Providers of models already on the market before 2 August 2025 have until 2 August 2027. The Commission’s AI Office gained active enforcement powers on 2 August 2026.
Do AI laws apply to developers or to deployers?
Both, but rarely the same obligations. EU GPAI duties bind model providers. EU Article 50 duties bind providers and deployers differently — providers mark output, deployers disclose deepfakes and chatbot interaction. Colorado splits developer documentation duties from deployer notice duties. Determining your role per system per jurisdiction is the first real step in any assessment.
Where should organisations verify an AI regulation?
At the primary source: EUR-Lex and the Official Journal for EU instruments, the Federal Register and agency sites for U.S. federal action, state legislature records for state law, and the relevant regulator for implementing rules. Secondary analysis is useful for interpreting complex provisions but should never be the basis for a date.
Keep reading
Here are the latest posts from the blog.
AI Compliance Deadlines: What Applies, When, and to Whom
AI Agent Framework Security: 10 Frameworks Audited
Cluster Topology Decides What You Can Actually Run