Your Robot May Pass Every Test. Its Simulator Could Still Be Lying

Robotics Cybersecurity

Last checked: 3 November 2026. Vulnerability identifiers, affected projects and patch information will be updated as coordinated disclosures become public.

A robot that clears every simulated obstacle course has earned a green row in a test report. That row is evidence, and evidence has a source. If the simulator, the scene files or the scripts that score the run have been tampered with, the robot hasn’t proved anything at all.

That’s the uncomfortable question behind VicOne’s announcement on 1 November. The Tokyo-based security company says AI-assisted research turned up 28 zero-day findings in under two days, and that about three-quarters sit in the tools used to develop, train, simulate and validate robots. For robotics cybersecurity, that shifts attention from the machine on the factory floor to the systems that decide it’s safe to put it there.

Key Takeaways
  • VicOne reports 28 AI-assisted zero-day findings in under two days. They’re vendor-reported and initially validated by the company, with no affected projects or CVEs published yet.
  • About 75% sit in development, training, simulation or validation tools. The exposed surface is the toolchain, not only the robot.
  • A compromised simulator can produce passing results for an unsafe robot. Simulation evidence needs integrity controls.
  • The remote-stop demo shows a software stop path can fail. It doesn’t show that hardwired emergency stops can be defeated.
  • Training artefacts and simulation assets are part of the supply chain. Poisoned models or meshes can carry problems into deployment.
  • Robotics cybersecurity covers the whole lifecycle, from repositories to fleet commands.
  • Reported, validated, CVE-assigned and patched are different states. None of the 28 has publicly reached the last two.
  • Teams should verify assets, repeat critical tests independently and keep a physical stop.

Quick Navigation


The 28 findings: what VicOne actually reported

The claim appeared in a sponsored post on The Robot Report. It describes “less than two days of AI-assisted research across software and tools that support the ‘Physical AI’ ecosystem,” including projects “developed or maintained by Google, NVIDIA and Meta.” It states: “Based on initial validation, all 28 findings are classified as zero-day vulnerabilities.”

Read that sentence carefully. “Zero-day” here is VicOne’s classification of flaws it believes were previously unknown. “Initial validation” is VicOne’s own. According to AI Weekly’s write-up, the post says the count may change after review, some findings “do not yet have CVE tracking numbers,” and the consequences it describes “are potential consequences and not demonstrated outcomes for every finding.”

The post doesn’t name an AI model or tool. It doesn’t say whether “less than two days” covers discovery alone or discovery plus human triage. It doesn’t identify a single affected repository, which is normal during coordinated disclosure. It also ends with a pitch for VicOne’s upcoming white paper and its products: Radeis, which the company sells for pre-deployment validation of AI robots, and Rthena, for runtime protection. VicOne has a commercial interest in showing that its discovery works. That doesn’t make the findings wrong. It means they should be treated as vendor-reported until maintainers or independent researchers confirm them.

Robotics cybersecurity tracker: the 28 findings
Tracker fieldInformation
Research organisationVicOne
Reported findings28
Discovery periodLess than two days, as reported
Initial classificationVendor-reported zero-day findings, based on VicOne’s initial validation
Pre-deployment tool shareAbout 75% (roughly 21 of 28), as reported
AI tools usedNot disclosed
Affected projectsNone publicly identified; the post refers to projects from Google, NVIDIA, Meta and others
CVE statusNo CVE publicly linked to the findings; some lack CVE numbers, per the post
Independent confirmationNone found
Patch statusNot disclosed
Last verified3 November 2026

This article will be updated when there are new CVE assignments, maintainer acknowledgements, published patches, severity scores, independent reproduction or a revised count.

Robotics cybersecurity begins before deployment

The detail worth more than the headline number is where the bugs sit. The post says that 75% of the findings “sit in development, training, simulation or validation tools,” rather than in software running on a deployed robot.

That doesn’t mean 21 vulnerabilities can each reach out and move a robot arm. A flaw in a training tool usually needs an attacker to get malicious input into the pipeline first: a poisoned dataset, a tampered model file, a crafted scene asset or access to a shared build machine. The impact depends on what the tool touches next. Code execution on a workstation is an IT problem. Code execution on a machine that writes the policy file shipped to a fleet is a robot problem, and that’s the gap robotics cybersecurity has to cover.

Where robotics cybersecurity meets the training pipeline

A modern robot’s behaviour is assembled long before it runs. Robot description files define its joints and geometry. Simulation assets define the world it learns in. Training jobs produce policy checkpoints. Validation scripts decide whether those checkpoints pass. Each step consumes files written by someone else, often downloaded from public repositories.

VicOne’s post gives an example of the stakes: a manipulated model could make a robot “respond incorrectly to a particular object, scene, or command after deployment.” That’s a description of a possible outcome, not a reported exploit. But the mechanism isn’t speculative. Pickle-based model files can execute code when loaded, which is why our guide on how to verify model weights before loading them treats format and provenance as separate checks.

When the simulator lies, the safety case breaks
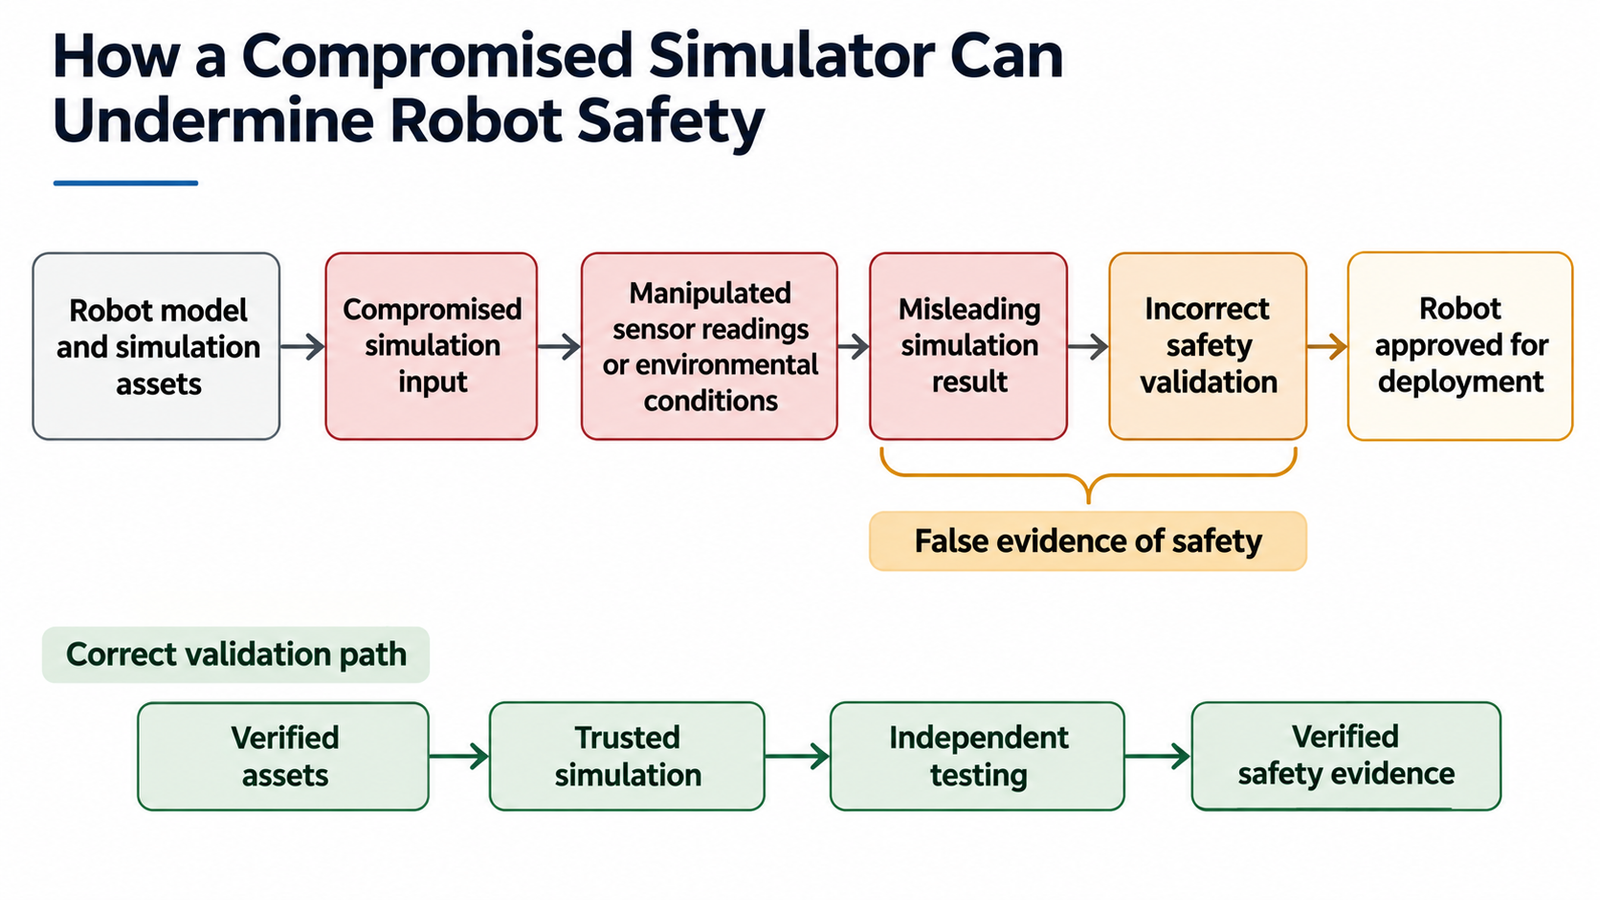
An illustrative attack path. Every stage after the compromise can look normal.

Simulation is where most modern robots earn their first approval. Teams run thousands of scenarios they could never stage physically, record pass rates and use those numbers in design reviews and safety arguments. The post’s own warning is blunt: a robot “could then appear to pass tests that should have exposed unsafe behavior.”

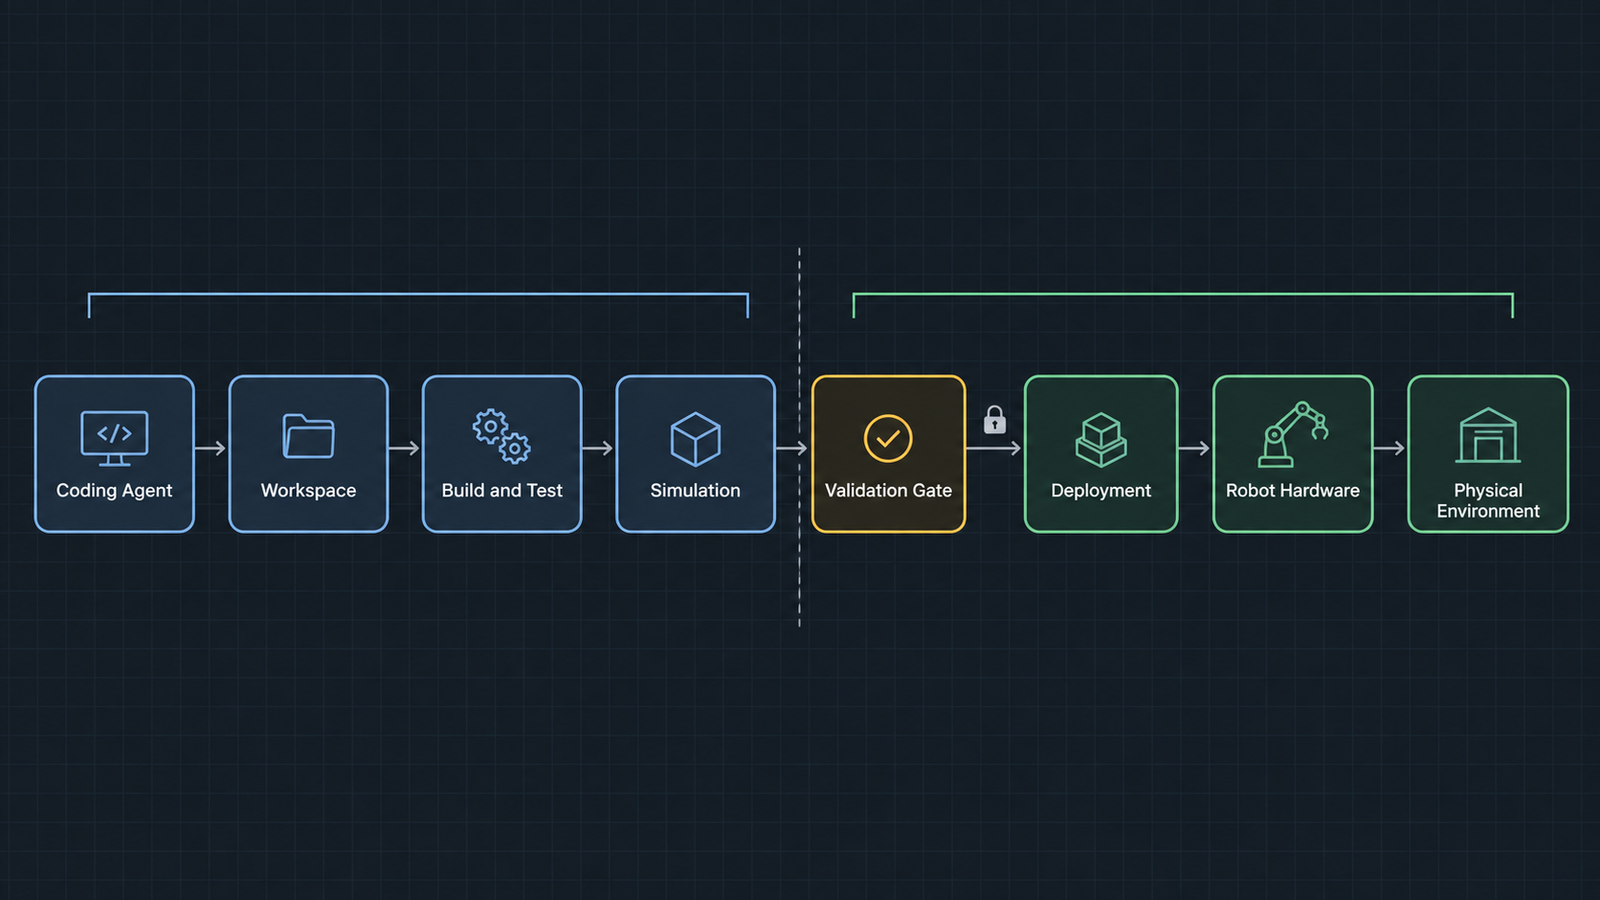
The chain is longer than most security reviews cover. Robot software is trained on data, tested in a simulator, scored by validation scripts and summarised as safety evidence. Engineers and auditors then make deployment decisions from that evidence. A compromise at any earlier link can be invisible at the last one, because the evidence looks exactly like a pass.

An illustrative robotics cybersecurity failure in simulation

This scenario is illustrative. It isn’t an incident VicOne or anyone else has reported.

A warehouse robotics team tests whether a mobile manipulator stops for a person stepping into an aisle. An attacker has altered a shared scene package so the simulated lidar returns are slightly delayed only when a human model enters from the left. Alternatively, the attacker has patched the scoring script to log a stop when the robot only slowed down. The robot “passes” 2,000 runs. The report goes to the safety review with a clean result, and nobody asks whether the simulator itself was the thing under test.

Published research shows how quiet this can be. In September, researchers described collision mesh poisoning. A 3D asset has a visual mesh for rendering and a collision mesh for physics. Altering only the collision mesh can produce policies that look normal in simulation and fail after deployment. The authors note that current asset reviews check for malware, licensing and format, not whether the two meshes agree.

This is where robotics cybersecurity parts ways with conventional IT security: the output is a decision about physical risk. A stolen password gets reset. A safety sign-off based on corrupted evidence can put a machine next to people. The principle is simple: a safety test is only as trustworthy as the system producing its evidence.

UniverseBlend made a similar point about AI model testing in Four Labs, One Evaluator, arguing that “the evaluator’s infrastructure needs the same scrutiny the industry currently applies to model behaviour.” The cases aren’t technically alike. One was about network containment during evaluations, the other is about simulation integrity. The shared lesson is that the system producing the evidence must itself be trustworthy.

What the remote-stop demo means for robotics cybersecurity

The one concrete artefact in the announcement is a video. VicOne’s post says “the researchers exploited a vulnerability to prevent a robot’s remote-stop command from working.” A VicOne video titled Robot Keeps Moving After STOP Is Pressed, credited to its LAB R7 research group, was posted on 11 October, three weeks before the 28-finding announcement. Its description doesn’t name the robot, the software stack or the vulnerability. VicOne hasn’t said whether the demo is one of the 28 findings.

The word that matters is “remote.” A remote-stop command is usually a software message sent over a network to the robot’s controller, through middleware, an API or a fleet manager. If an attacker can block, delay or spoof that message, the command never arrives. That’s serious, and it’s a cybersecurity failure.

A safety-rated emergency stop is a different thing. Under IEC 60204-1 and ISO 13850, an emergency stop must take priority over all other functions in every operating mode. It’s typically implemented through safety-rated hardware that cuts or controls drive power independently of the application software. UniverseBlend’s analysis of Isaac ROS 5.0 and the robotics agent boundary made the same point: e-stops sit below the ROS layer.

Nothing public suggests VicOne defeated a hardwired emergency stop, and the demo shouldn’t be read as showing that all emergency stops can be disabled. It does show something that matters: some deployments rely on software stop paths as a practical safety measure, and those paths need to be authenticated, monitored and backed by an independent physical stop.

Shared tools turn robotics cybersecurity into a supply-chain problem

Robotics runs on a small number of shared foundations: ROS 2 for middleware, simulators such as Gazebo and NVIDIA Isaac Sim, NVIDIA’s Isaac ROS packages, open training frameworks and public repositories of robot models and assets. VicOne hasn’t named any affected project, and being part of this ecosystem doesn’t make a project vulnerable. But when a shared tool has a flaw, every team that uses it inherits the exposure, so robotics cybersecurity depends partly on code nobody on the team wrote.

Independent records show the toolchain is a real target. CVE-2026-25874, published in April and unrelated to VicOne, covers Hugging Face’s LeRobot through version 0.5.1. Its policy server and robot client used pickle.loads() on data received over unauthenticated gRPC without TLS, allowing remote code execution. It’s rated 9.3 (critical) under CVSS 4.0.

Configuration matters as much as code. ROS 2’s security layer, SROS 2, is off by default. Even when enabled, its default “permissive” strategy launches a node without security if its security files are missing. Teams that want enforcement must set the “Enforce” strategy explicitly. A 2018 scan of the internet for ROS found robots reachable from the public internet. With consent, the researchers read camera data from a university robot and moved it.

AI-assisted discovery: faster robotics cybersecurity research, harder response

AI-assisted vulnerability research usually means models reading code, spotting dangerous patterns, tracing how untrusted data flows into risky functions and drafting proof-of-concept inputs. Humans still decide whether a crash is exploitable, rate severity, write the report and handle disclosure.

The approach has a track record, with caveats. Google’s Big Sleep agent found an exploitable flaw in SQLite before it reached a release in 2024. Its team called the results “highly experimental” and said a target-specific fuzzer was likely at least as effective. In May 2026, Google’s threat intelligence group reported that attackers had used AI to find and exploit a zero-day for a planned mass-exploitation campaign.

That second case is the uncomfortable symmetry. If a defender can surface 28 candidate flaws in two days, an attacker with similar tools can too. Discovery speeds up; patching doesn’t. Many robotics tools are maintained by small teams or research groups. Fixes then have to travel through pinned versions, container images and robot fleets that update slowly. The bottleneck moves from finding bugs to absorbing them.

What Robotics Teams Should Check Now
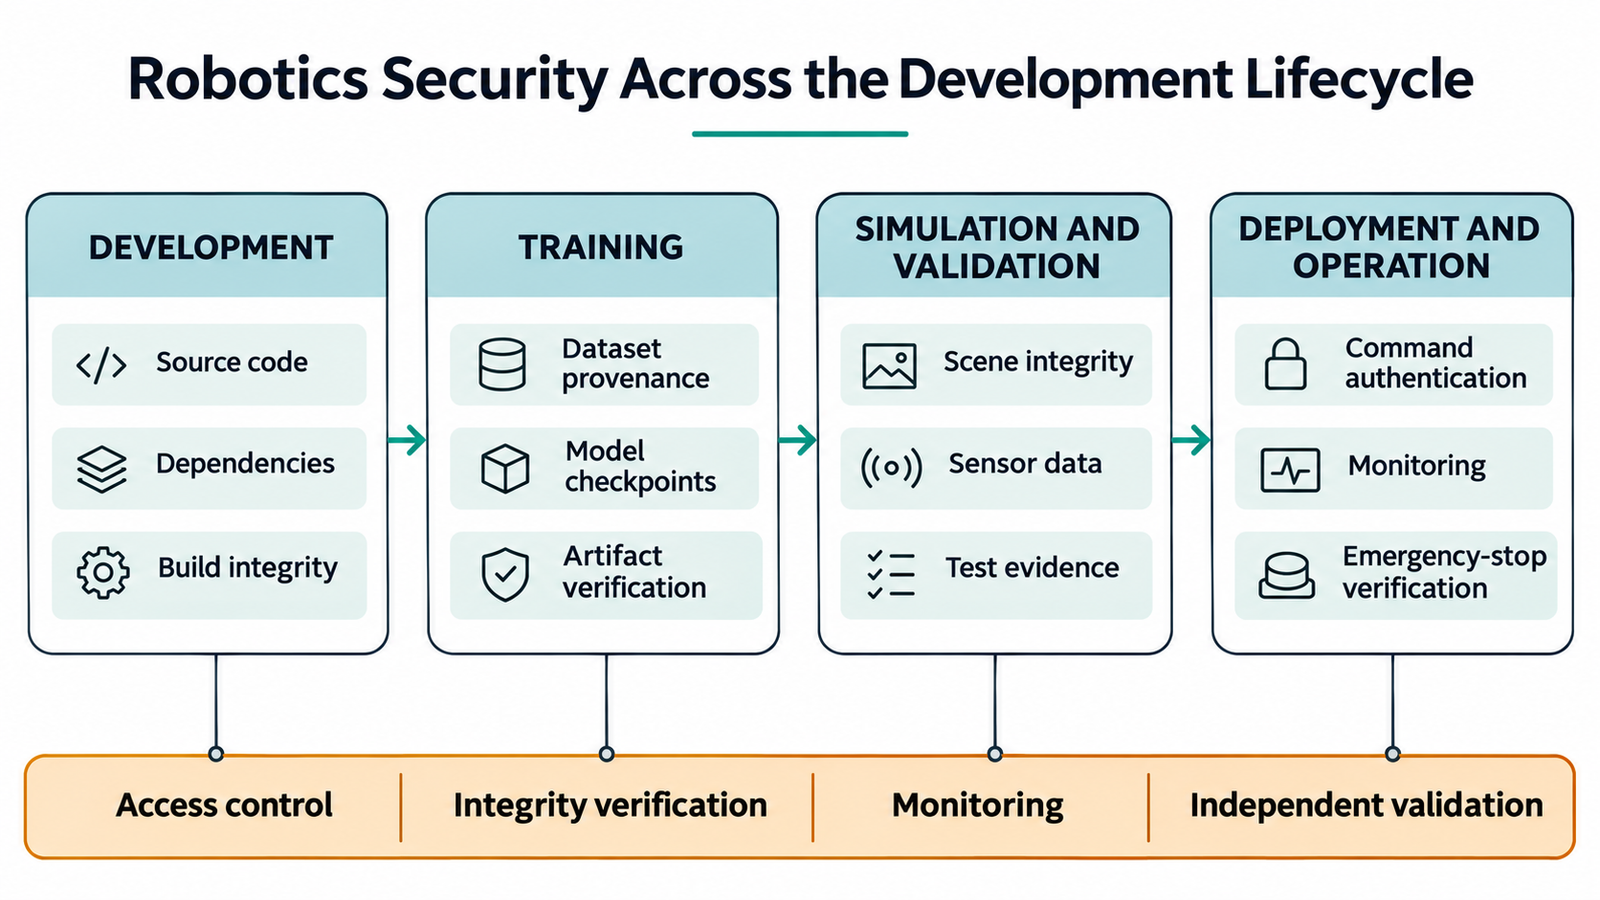
Security controls have to cover the tools that build and test a robot, not only the robot.

These are practical robotics cybersecurity checks, not a certified safety standard. They don’t replace functional-safety requirements such as ISO 10218, ISO 13849 or IEC 61508 where they apply.

1. Development environment

  • Protect repositories with signed commits and branch protection.
  • Pin dependencies and record where each one came from.
  • Limit who and what can trigger builds.
  • Validate model files before loading them.
  • Restrict access to training machines.

2. Training pipeline

  • Record dataset provenance.
  • Hash model checkpoints and other training artefacts, and verify them at each handoff.
  • Separate access between data, training and release.
  • Make runs reproducible enough to repeat when results look wrong.

3. Simulation environment

  • Version-control scenes, robot descriptions and simulator configurations.
  • Hash simulation assets and check that visual and collision geometry agree.
  • Treat simulator plugins and dependencies as code that needs review.
  • Protect test logs and results from modification.

4. Validation process

  • Keep known-good baselines and run safety regression tests against them.
  • Repeat key scenarios on a second, independently built environment.
  • Confirm critical behaviours physically, not only in simulation.
  • Have a person review anomalies rather than only pass rates.

5. Deployment and operation

  • Segment robot networks.
  • Authenticate commands; for ROS 2, enable SROS 2 in Enforce mode.
  • Give fleet tools least-privilege access.
  • Monitor command and telemetry paths.
  • Verify that a physically independent emergency stop works.
  • Confirm patches actually landed on every robot.

Robotics cybersecurity questions VicOne hasn’t answered yet

Several questions decide whether this is a significant disclosure or a strong marketing demonstration:

  • Which Google, NVIDIA and Meta projects are affected, and at what severity?
  • Which AI tools did the work, and how much human validation followed?
  • Does “less than two days” include triage?
  • Is the remote-stop demo one of the 28, and has it been fixed?
  • Will maintainers confirm the reports, and will independent researchers reproduce them?

Until advisories or CVE records appear, the honest position is that 28 findings have been reported and none has been publicly confirmed. The checks above don’t depend on the answer, though. For robotics cybersecurity teams, they’re worth doing either way.

Frequently asked questions

What is robotics cybersecurity?

Robotics cybersecurity protects robots and the systems around them, including development tools, training pipelines, simulators, networks and command paths, from attacks that could affect data or physical behaviour.

What did VicOne’s robotics cybersecurity research find?

VicOne says AI-assisted research found 28 zero-day findings in under two days, mostly in development, training, simulation and validation tools. The findings are vendor-reported and not yet publicly confirmed.

Why are development tools a robotics cybersecurity risk?

They produce the code, models and test results that determine how a robot behaves. A compromised tool can pass tampered output downstream without any change to the robot itself.

How can a compromised simulator affect robot safety?

It can alter scenes, sensor data or scoring so an unsafe robot appears to pass. Teams may then approve deployment based on misleading evidence.

How does physical AI security differ from robotics cybersecurity?

Physical AI security focuses on AI systems that sense and act in the physical world, including model and perception attacks. It overlaps heavily with robotics cybersecurity, which also covers conventional software, networks and hardware.

How does AI help researchers discover software vulnerabilities?

AI models can read code, flag risky patterns, trace data flows and draft test inputs quickly. Humans still confirm exploitability, assess severity and handle disclosure.

Why are robotics training pipelines vulnerable to attacks?

They consume datasets, model files and assets from many sources, often with little integrity checking. Poisoned inputs can change learned behaviour in ways tests may not reveal.

What should teams do to improve robotics cybersecurity now?

Verify dependencies, models and simulation assets, protect test evidence, repeat critical tests independently, authenticate robot commands and keep a physical emergency stop.

Are the 28 VicOne findings assigned CVE numbers?

Not publicly, as of 3 November 2026. VicOne says some findings don’t yet have CVE numbers, and none of the 28 has been publicly linked to a CVE record.ntainer with no credentials, no network and resource limits, while watching what it does.


Keep reading

AGI vs superintelligence

AGI vs Superintelligence: A New Name Isn’t a New Intelligence
Facts checked against official documents and reporting on 18 November 2026. On 29 September, the White House told federal agencies to stop writing “artificial intelligence” …
AI Coding Agent

AI Coding Agents Are Getting Expensive. Who’s Paying for the Tokens?
Pricing checked on official vendor pages on 17 November 2026. All USD. Cost scenarios are illustrative and labelled as such. On 28 October, TechCrunch published …
Model Weights

Verify Model Weights: 7 Checks Before You Download
Checked against the burner22/numbat repository and its discussions, Hugging Face and PyTorch documentation, and Moonshot AI’s announcement on 2 November 2026. On 1 November, a …
Agentic AI Statistics

30 Agentic AI Statistics for 2026: Adoption, Spending and Risk

Last updated: 15 November 2026. This page is updated monthly; each figure keeps its original publication date. Agent traffic at one healthcare booking platform rose …

Isaac ROS 5.0 and the Robotics Agent Boundary Problem

Isaac ROS 5.0

One of the agent skills NVIDIA published alongside Isaac ROS 5.0 is called submit-and-monitor-mission. Its documented sample prompt reads: submit a route mission to carter01 and prove it actually completed.

That is not autocomplete. That is a coding assistant issuing a task to a robot in a fleet and verifying the outcome, from a chat window.

NVIDIA released Isaac ROS 5.0 on September 21, 2026, announcing it at ROSCon in Toronto the following day. Most coverage has focused on the ROS 2 Lyrical migration and the NITROS rewrite, both of which matter to anyone maintaining an Isaac ROS workspace. The more interesting change is quieter: robotics development tasks are now packaged as structured skills that AI coding assistants can invoke.

Which raises a question the release notes do not answer, because it is not NVIDIA’s to answer. When an agent works on software that eventually moves actuators, what should it be allowed to reach?

Key takeaways
  • Isaac ROS 5.0 ships AI agent skills in the open Agent Skills format, including isaac-ros-activate for the development environment and an early-access skill for migrating nodes off NITROS.
  • Separately, the Mission Control documentation publishes five skills that reach further, including submitting missions to robots and changing fleet composition.
  • The release moves to ROS 2 Lyrical Luth on Ubuntu 24.04 and rebuilds the accelerated data path on rosidl::Buffer. Code calling NITROS APIs directly needs source-level migration.
  • Isaac ROS 5.0 does not give an agent control of a robot. It gives an agent structured access to the toolchain that produces robot software, which is a different thing with its own permission questions.
  • The useful boundary in agentic robotics is not the IDE. It runs across repository, build, simulation, middleware, deployment and hardware, and each of those deserves a separate permission decision.

Quick Navigation


What Isaac ROS 5.0 Actually Adds

Isaac ROS is NVIDIA’s collection of CUDA-accelerated packages built on open-source ROS 2. It is not a replacement for ROS 2 and not a robot controller. It supplies GPU-accelerated perception, localisation, planning and deployment packages that run inside a ROS 2 graph.

Four changes define the 5.0 release, all documented in NVIDIA’s release notes.

  1. ROS 2 Lyrical Luth becomes the supported distribution, with a Buildfarm apt repository carrying ROS 2 Lyrical ecosystem packages for Ubuntu 24.04 Noble.
  2. The accelerated data path was rebuilt. NITROS now sits natively on ROS 2 Lyrical’s rosidl::Buffer with the CUDA buffer backend, letting accelerated nodes exchange standard ROS messages whose array fields can be backed by GPU memory. The NITROS packages themselves were removed. Code that called NITROS APIs or types directly requires source-level migration; isaac_ros_nitros_bridge_ros2 survives as a deprecated bridge marked for removal.
  3. AI agent skills arrive in the open Agent Skills format. The Isaac ROS CLI ships isaac-ros-activate for activating the development environment, plus an early-access migrate-node-to-rosidl-buffer skill for moving a node off the NITROS APIs. NVIDIA says further Isaac skills are published in the nvidia/skills catalog under the Physical AI category.
  4. GPU partitioning became a package. isaac_ros_gpu_partitioning assigns a fixed share of a GPU’s streaming multiprocessors to each ROS 2 process using CUDA Multi-Process Service. NVIDIA is explicit about its limits: it does not partition GPU memory and does not isolate workloads.

That last sentence is worth noting, because it is the kind of precision the rest of this discussion needs. Partitioning compute is not isolation, and NVIDIA says so plainly rather than letting readers assume otherwise.

The release also renames isaac_ros_visual_slam to isaac_ros_cuvslam, changes the teleop end-effector pose topic type in a way that breaks existing subscribers, and carries a frank list of limitations — RealSense cameras supported only in Docker mode, an H.264 encoder segfault on shutdown on Jetson Thor with VPI 4.1.4, cuMotion MoveIt examples that may fail against robot vendor packages not yet certified for Lyrical.

A migration, in other words. A substantial one.


From Code Assistant to Robotics Toolchain Agent

The difference between autocomplete and agentic development is not the quality of the code. It is whether the tool acts.

Autocomplete proposes text and a human commits it. An agentic workflow runs commands, reads output, decides what to do next, and repeats until a stated goal is met or it gives up. The skill format is what makes that repeatable: it packages a procedure, its preconditions and its verification steps so the agent follows a known path instead of improvising one.

NVIDIA’s Mission Control documentation gives the clearest picture of what that looks like in robotics. It lists five published skills, installable through a single npx skills add command, and states they work with Claude Code, Cursor, Codex and other Agent Skills clients.

SkillWhat it does
bring-up-cloud-stackStarts the Mission Control cloud services from the repository compose stack
change-mapChanges the map Mission Control loads, including from an uploaded file, URI or S3 object
change-fleet-compositionAdds, removes, renames or relabels robots in the fleet
change-stack-versionChanges the image tag of any Mission Control service
submit-and-monitor-missionSubmits a mission and verifies it completed end to end

Read that list as a permission surface rather than a feature list. Starting services, changing which map a fleet navigates against, altering fleet membership, pinning service versions, dispatching missions. In a conventional software context these would be infrastructure operations requiring review. Here they are chat prompts.

None of this is hidden or oversold. NVIDIA documents each skill with a sample prompt and notes the combination case: change the map, add an AMR, restart the stack, run a health check. It reads exactly like a DevOps runbook, which is the point.


The Isaac ROS 5.0 Boundary Question Is Not the IDE

The question worth asking is not whether an AI agent can write ROS 2 code. It can, adequately, and Isaac ROS 5.0 makes it better at the Isaac-specific parts by giving it documented procedures.

The question is what the agent can reach after the code exists.

Here is the chain, and it helps to keep the layers distinct, because collapsing them into “AI controls robots” produces bad reasoning in both directions:

  • AI coding agent — writes and modifies source, runs commands, reads results. Has no real-time guarantees and no place in a control loop.
  • Isaac ROS — GPU-accelerated ROS 2 packages for perception, localisation and planning.
  • ROS 2 middleware — the message transport connecting nodes.
  • Robot autonomy stack — the assembled graph that decides what the robot does.
  • Robot controller — the real-time layer commanding joints and wheels, typically with its own safety functions.
  • Isaac Sim — the simulator, a separate application from Isaac ROS.

An agent editing a launch file is operating at layer one. The effect of that edit can propagate to layer five. The propagation is not instantaneous or automatic, and the gates between layers are where the engineering decision sits.

Risk changes at each step:

BoundaryWhat the agent doesWorst realistic outcome
Source codeEdits packages, configs, launch filesA bad change sits in a branch
DependenciesInstalls packages, changes versionsSupply-chain exposure, broken builds
BuildCompiles the workspaceWasted time; a binary that behaves differently than reviewed
SimulationLaunches Isaac Sim scenariosMisleading pass results
MiddlewarePublishes to live ROS 2 topicsInterference with a running system
DeploymentPushes artifacts to robot computeUntested software on a machine
HardwareCommands actuatorsPhysical consequences
Isaac ROS 5.0

The first three are ordinary software risks with ordinary controls. The last three are not, and treating them as one continuous permission level is the mistake worth avoiding.


What Does Egress Control Look Like in a Workcell?

In conventional agentic development, sandboxing means protecting files, credentials, processes and network access. Those concepts map onto robotics, but imperfectly, and the places where the analogy breaks are the interesting ones.

Software agent controlRobotics equivalentWhere the analogy breaks
Filesystem permissionsWorkspace, packages, launch and config filesConfig changes can alter physical behaviour without touching code
Credential scopeRobot, fleet and deployment credentialsA fleet credential can address many machines at once
Network egressWhich robots, fleet services and telemetry endpoints are reachableROS 2 discovery is permissive by default; a node on the same network can find peers
Process executionROS 2 nodes and launch filesA launched node publishes to a live graph, not just to stdout
SandboxSimulation or an isolated workcellA simulator is a model, not a copy
Deployment approvalPhysical deployment approvalRollback restores software, not a dropped payload

The closest robotics analogue to network egress control is the set of decisions about what the development environment can address. ROS 2 nodes on a shared network discover each other by default, which means an agent that can launch a node can potentially participate in a graph that includes real hardware unless something prevents it. Domain ID separation, network segmentation and DDS configuration are the mechanisms that do the preventing.

Cloud-connected fleets sharpen this. Mission Control dispatches missions over network services, and the VDA5050 protocol exists precisely so fleet managers can command robots from elsewhere. Once an agent can reach that interface, network reachability is the control that matters, exactly as it is for any other agent workflow — a point we worked through in our piece on testing agents against prompt injection, where reachability rather than instruction quality decided the outcomes.

The mechanisms that can be technically substantiated, without inventing capabilities:

  • Separate ROS 2 domain IDs and network segments for development, simulation and production
  • DDS security configuration where the deployment supports it
  • Credential scoping so development credentials cannot address production fleets
  • Deployment gates requiring signed, versioned artifacts rather than direct file copies
  • Simulation-only execution modes for agent workflows
  • Emergency stop and safety functions implemented independently of the software stack
  • Rollback to a known-good artifact version

That last pair deserves emphasis. E-stop circuits and safety controllers exist below the ROS layer precisely so that no software fault, agent-introduced or otherwise, can defeat them. NVIDIA documents a safety controller concept within isaac_ros_deploy, with its own troubleshooting guide, which reflects the same layered thinking.


Simulation Is a Boundary, Not a Guarantee

Restricting an agent to simulation is the single most useful control available, and it is genuinely strong: a mistake in Isaac Sim costs compute time, not equipment.

It is also not proof of physical safety, for reasons every robotics engineer already knows and every agentic workflow will rediscover.

Simulators model contact, friction, sensor noise, latency and timing approximately. The sim-to-real gap is a permanent feature of the field, not a bug awaiting a fix. A perception model tuned in simulation encounters real lighting, real motion blur and real camera calibration error. A grasp that succeeds against a simulated object may slip on the real one.

There is a second-order problem specific to agents. An agent optimising for a simulated success metric will find whatever satisfies that metric, including artefacts of the simulation itself. That is reward hacking in a new costume, and it argues for holdout scenarios the agent has not been iterating against.

The practical sequence most teams already use stays intact:

  1. Simulation for broad coverage and fast iteration
  2. Replay against recorded sensor data, which tests perception against real inputs deterministically
  3. Hardware-in-the-loop, with real compute and real timing but constrained motion
  4. Supervised physical testing in a controlled cell
  5. Production deployment

An agent can usefully operate through step two. Steps three onward are where human judgement earns its place, and no part of Isaac ROS 5.0 suggests otherwise.


Failure Modes Change When Code Reaches Hardware

Software failures are usually graded by how loud they are. In robotics they should be graded by where they surface.

  1. Build failure. The workspace does not compile. Harmless, immediate, self-announcing. The best kind.
  2. Configuration failure. A launch parameter, calibration file or frame ID is wrong. This is the quiet one. A wrong camera extrinsic produces a system that runs cleanly and perceives the world offset by several centimetres. Nothing errors. Isaac ROS 5.0’s own release notes carry an instructive example: an occupancy grid localizer launch failure caused by empty frame IDs, fixed by using the named static_transform_publisher arguments Lyrical requires. Configuration is where correct-looking code goes wrong.
  3. Runtime software failure. A node crashes. In a well-designed system a supervisor restarts it or the robot halts. The severity depends entirely on what the node was doing and what depends on it.
  4. Perception failure. The system misinterprets the world — a missed obstacle, a bad pose estimate. It does not announce itself, and downstream components act on the wrong belief with full confidence.
  5. Planning failure. A trajectory is generated that is valid in the planner’s model and wrong in the world, typically because the model of the environment was wrong.
  6. Control failure. The lowest and most consequential layer, which is exactly why safety functions live below it and independent of it.
  7. Deployment failure. The wrong version reaches the robot, or reaches some robots in a fleet and not others. Version skew across a fleet is its own category of problem, and change-stack-version existing as an agent skill is a reason to think about it now rather than later.

The ordering that matters for permissions: failures that announce themselves are cheap; failures that propagate silently into physical action are not. An agent workflow should be designed so its mistakes land in the first category.


How to Evaluate Agentic Development in an Isaac ROS 5.0 Workflow

Benchmark scores on coding tasks say little about whether an agent is safe to run in a robotics toolchain. A complete picture needs measures from three groups.

Did it work?

  • Task success against a stated goal
  • Code correctness, by review and by test
  • Regression rate across the existing test suite
  • Simulation success, on scenarios the agent has not been iterating against
  • Reproducibility across repeated runs from the same starting state

How did it behave?

  • Tool-call accuracy: did it invoke the right commands with the right arguments
  • Permission violations: attempts to act outside its granted scope, which should be logged whether or not they succeeded
  • Unsafe configuration attempts: disabled safety parameters, widened velocity limits, bypassed checks
  • Escalation behaviour: does it stop and ask, or improvise, when blocked

What happens when it is wrong?

  • Rollback success rate and time to restore a known-good version
  • Human approval compliance: did anything reach a gated stage without approval
  • Auditability: can every action be reconstructed from logs afterwards

The second and third groups are the ones benchmarks skip. An agent with a 90% task success rate that occasionally tries to widen a velocity limit to make a test pass is worse than one at 75% that stops and asks. The containment-versus-capability trade is the same one we examined in our analysis of evaluator access and security boundaries, and it resolves the same way: measure what the system does when it cannot get what it wants.


What Isaac ROS 5.0 Means for Physical AI Teams

The release lands differently depending on what you do with it.

  • Robotics developers get a real migration and a tool that helps with it. Moving off the NITROS APIs is mechanical, repetitive work across many files — precisely the shape of task agents handle well, which is presumably why NVIDIA shipped migrate-node-to-rosidl-buffer alongside the change that requires it. It is marked early access, so treat its output as a first pass to review rather than a finished migration.
  • AI engineers get an entry point into robotics that does not require learning the whole stack first. This cuts both ways. The skills encode NVIDIA’s intended procedure, which is better than an agent improvising. They also make it easy to operate parts of a system you do not yet understand.
  • Robotics teams get a permissions question they probably have not formalised. Most teams have conventions rather than enforced boundaries around who can deploy to which robot. An agent that follows documented procedures faster than any human will surface the gap between convention and control.
  • Platform engineers get the ROS 2 Lyrical and Ubuntu 24.04 move, the Buildfarm repository, and GPU partitioning via CUDA MPS — with NVIDIA’s own caveat that partitioning is not isolation.
  • Safety engineers get the most important reminder in the release: nothing here changes where safety functions live. E-stop circuits, safety controllers and certified components sit below the ROS layer and remain independent of it. Isaac ROS 5.0 does not give an AI agent control of a robot. It gives an agent structured access to the toolchain that produces robot software.

Those are different claims, and the distinction is worth defending whenever the coverage blurs it.


Questions to Ask Before an Isaac ROS 5.0 Agent Touches a Robot

Ten questions. If your team cannot answer them, the answer to “should we give an agent access” is not yet.

  1. What can the agent read? Source, configs, calibration files, recorded data, credentials?
  2. What can it modify? Which repositories, packages, launch files and parameter files, and which are off limits?
  3. What can it execute? Build commands, dependency installation, node launches, simulation, deployment scripts?
  4. What can it deploy, and where? Development machines, a test robot, a fleet?
  5. What hardware can it reach? Directly, and indirectly through fleet services and cloud interfaces?
  6. What network destinations can it access? Package repositories, model registries, robot networks, telemetry endpoints?
  7. What happens when simulation and reality diverge? Who notices, and what stops the change from progressing?
  8. Where is human approval mandatory? Name the specific gates rather than the principle.
  9. Can every action be audited? Commands, file changes, deployments, and refused attempts.
  10. Can changes be rolled back? Including configuration and calibration, not just code.

There is no universal answer to where the approval boundary belongs. A mobile robot in a warehouse aisle, a manipulator behind a fence and a humanoid working near people have different consequence profiles, and the right gate depends on the robot, the environment, the autonomy level and the deployment architecture.

What Isaac ROS 5.0 changes is the urgency. The skills exist, they are documented, they install in one command, and they work with the coding assistants your team already uses. The permission model is now the part of the toolchain that needs designing.


Frequently Asked Questions

What is Isaac ROS 5.0?

Isaac ROS 5.0 is the September 2026 release of NVIDIA’s collection of CUDA-accelerated packages built on open-source ROS 2. NVIDIA tagged the 5.0.0 packages on September 21, 2026 and announced the release at ROSCon in Toronto on September 22. It moves to ROS 2 Lyrical Luth on Ubuntu 24.04, rebuilds the accelerated data path on rosidl::Buffer, and adds AI agent skills.

What are AI agent skills in Isaac ROS 5.0?

They are documented procedures in the open Agent Skills format that AI coding assistants can follow. The Isaac ROS CLI ships isaac-ros-activate for the development environment and an early-access migrate-node-to-rosidl-buffer skill. NVIDIA publishes further skills in the nvidia/skills catalog, and the Mission Control repository publishes five more covering cloud stack startup, map changes, fleet composition, service versions and mission submission.

Does Isaac ROS 5.0 let AI agents control robots?

No. It gives agents structured access to robotics development workflows — environment setup, migration, and Mission Control operations. Robot control remains the job of the autonomy stack and the real-time controller, with safety functions implemented independently of the software stack. What an agent can reach in any given deployment depends on the permissions and network access that team grants it.

What is the relationship between Isaac ROS and ROS 2?

Isaac ROS is built on open-source ROS 2 and runs inside a ROS 2 graph. It supplies GPU-accelerated nodes for perception, localisation, planning and deployment. ROS 2 supplies the middleware, message types and tooling. Isaac ROS 5.0 supports ROS 2 Lyrical Luth.

What is the difference between Isaac ROS and Isaac Sim?

Isaac ROS is a set of ROS 2 packages that run on the robot or on development hardware. Isaac Sim is a separate simulation application. Many Isaac ROS tutorials use Isaac Sim as a data source, but they are distinct products.


Keep reading

AGI vs superintelligence

AGI vs Superintelligence: A New Name Isn’t a New Intelligence

Facts checked against official documents and reporting on 18 November 2026. On 29 September, the White House told federal agencies to stop writing “artificial intelligence” …
AI Coding Agent

AI Coding Agents Are Getting Expensive. Who’s Paying for the Tokens?

Pricing checked on official vendor pages on 17 November 2026. All USD. Cost scenarios are illustrative and labelled as such. On 28 October, TechCrunch published …
Model Weights

Verify Model Weights: 7 Checks Before You Download
Checked against the burner22/numbat repository and its discussions, Hugging Face and PyTorch documentation, and Moonshot AI’s announcement on 2 November 2026. On 1 November, a …
Agentic AI Statistics

30 Agentic AI Statistics for 2026: Adoption, Spending and Risk

Last updated: 15 November 2026. This page is updated monthly; each figure keeps its original publication date. Agent traffic at one healthcare booking platform rose …